NEN 7510 awareness training: what the standard and the IGJ ask (2026)
CyberPulse · Last updated: 15 November 2026
At a glance
NEN 7510 calls for appropriate awareness, education and training in healthcare. The Dutch inspectorate, IGJ, expects evidence that it works. An organisational certificate is not legally mandatory; regular independent assessment is.
Protecting patient data also depends on safe behaviour at reception, on the ward and on the move. Training should reflect that working environment.
What does NEN 7510 ask for?
Use NEN 7510-1:2024 and NEN 7510-2:2024, checking any transition arrangements relevant to your certification. The controls are in part 2. Control 6.3 covers awareness, education and training, with relevant content and regular updates.
Include people for whom the controls are relevant: care professionals, support staff, IT and relevant external workers such as locums and agency staff. Define the audience by access, work and risk, rather than employment contract alone.
The structure aligns with ISO 27002:2022. This can support a shared training approach for ISO 27001 and NEN 7510, provided healthcare-specific risks are addressed too.
Which situations should your team recognise?
Choose situations that reflect the job:
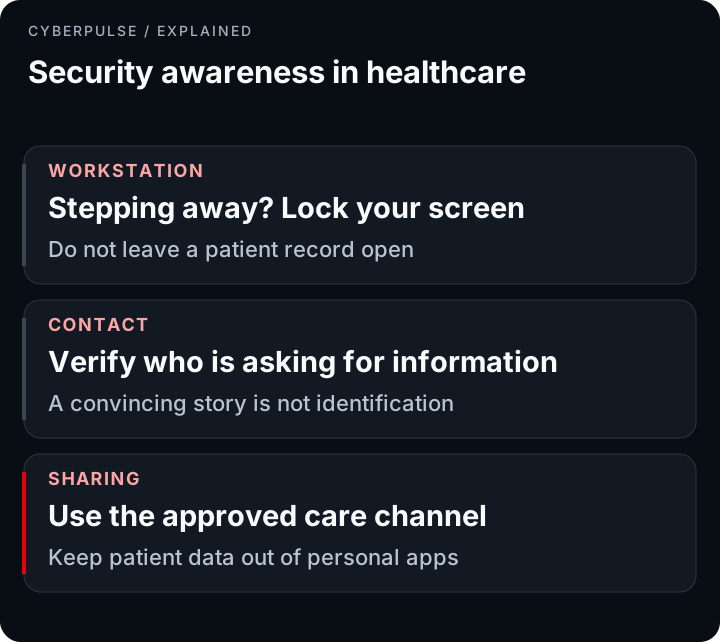
- An open patient record: a staff member is called away and locks the workstation.
- A convincing caller: reception checks identity and authority before disclosing information.
- A familiar patient: someone accesses a record only when their task justifies it.
- Working on the move: a community nurse shields the tablet and uses approved connections and apps.
These are training examples, not additional requirements. A common foundation can be combined with specialist content for clinicians, reception staff and administrators.
What does IGJ expect?
IGJ describes NEN 7510 as the statutory information security standard for healthcare providers processing personal data in healthcare information systems. Small practices must also demonstrate that they work according to it. IGJ identifies a different route through ISO 27001 for youth care.
Certification is not mandatory. You do need a functioning ISMS and evidence that controls work. IGJ specifies independent assessment at least once every three years; changes and risks may require more frequent assessment. This is not a training interval.
An assessor therefore looks beyond a training invoice: what was planned, who participated, what was learned and what improved?
How do you demonstrate training?
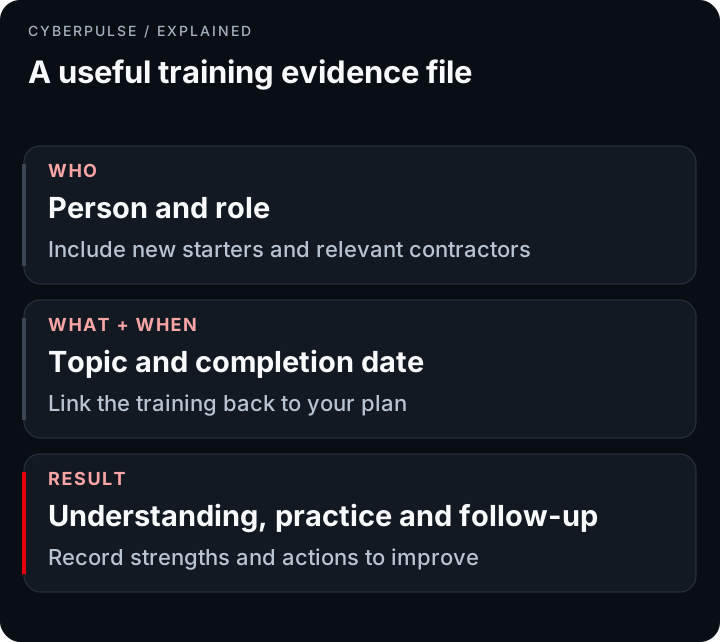
Keep a training plan, participation records and individual outcomes. Assess understanding with questions or exercises and use findings to improve. A phishing simulation can help, but is not the entire awareness programme.
Record how you cover starters, locums and role changes. An up-to-date staffing list and a training register that is months behind tell two different stories.
How to organise it
- Identify risks. Start with patient records, data exchange and continuity of care.
- Choose audiences and objectives. Connect them to daily activities.
- Train on joining and repeat. Include policy changes and new threats.
- Record and evaluate. Keep results and actions for independent assessment.
CyberPulse supports lessons, quizzes, phishing simulations and individual records. Combine that foundation with your own healthcare procedures. Find a partner. See also how training can support appropriate measures under the GDPR.
Frequently asked questions
Is NEN 7510 legally mandatory?
IGJ expects compliance from healthcare providers processing personal data in healthcare information systems, including small practices. Organisational certification is not mandatory; demonstrable operation and independent assessment are.
What changed with NEN 7510-1:2024?
The current parts are NEN 7510-1:2024 and 7510-2:2024. Controls in part 2 align with ISO 27002:2022. Check transition arrangements for existing certification.
How often must an independent assessment take place?
IGJ specifies at least once every three years. Risks or changes may call for more frequent assessment. This is an assessment interval, not a training interval.
Must all employees take an awareness training course?
Include people for whom the controls are relevant, based on access, activities and risks. Remember locums, agency workers and other relevant external staff.
What is the difference between NEN 7510 and ISO 27001?
ISO 27001 is a general information security management standard. NEN 7510 addresses Dutch healthcare. Evidence can overlap, but healthcare-specific requirements and risks still need coverage.
How do I demonstrate that my team is trained?
Keep a training plan, individual records, appropriate results and improvement actions. Show how new starters, external workers and role changes are included.
Sources
You get CyberPulse through a partner: find a partner · MSP or IT partner? See the partner programme